MICROSOFT 365 ASSESSMENTS
Know what needs attention before the next investment.
Focused reviews of security, identity, governance, licensing, and AI readiness, with prioritized remediation guidance and a follow-up consultation.
01
AI READINESS
Copilot & AI Readiness
Evaluates whether your Microsoft 365 environment is ready to safely adopt Copilot and AI tools by reviewing key controls for consent, workload identities, sharing, and sensitivity labels.
02
AGENT IDENTITY
AI Agents & Non-Human Identity
Identifies Copilot, AI agent, app registration, service principal, and other non-human identity risks across Microsoft 365, Entra ID, and Azure.
03
SECURITY BASELINE
Microsoft 365 Baseline Security
Reviews foundational Microsoft 365 security controls, including identity, MFA, Conditional Access, admin access, email security, logging, and external sharing.
04
DATA GOVERNANCE
Security & Data Governance
Includes everything in the Baseline Security assessment + assesses how Microsoft 365 protects, governs, labels, retains, and shares sensitive business data across users, groups, sites, and collaboration tools.
OPTIONAL ADDENDUM
Cyber Insurance Evidence Pack
Maps observed Microsoft 365, Entra ID, Defender, Copilot, AI agent, and non-human identity findings to common cyber insurance underwriting themes, clearly identifying verified evidence, exceptions, and areas requiring client attestation.
INSIDE YOUR ASSESSMENT
Actionable Insights.
Clear Priorities. Measurable Impact.
Our Microsoft 365 security assessments deliver a comprehensive view of your risk posture, highlights what matters most, and provides a practical roadmap for improvement.
STRATEGIC CLARITY FOR IT LEADERS
We translate complex Microsoft 365 security controls into business-focused insight so you can reduce risk, strengthen controls, and drive results.
INSIDE YOUR ASSESSMENT
Actionable Insights. Clear Priorities. Measurable Impact.
Our Microsoft 365 security assessments deliver a comprehensive view of your risk posture, highlights what matters most, and provides a practical roadmap for improvement.
STRATEGIC CLARITY FOR IT LEADERS
We translate complex Microsoft 365 security controls into business-focused insight so you can reduce risk, strengthen controls, and drive results.
1. Executive Summary
High-level view of your overall risk posture across key Microsoft 365 areas.
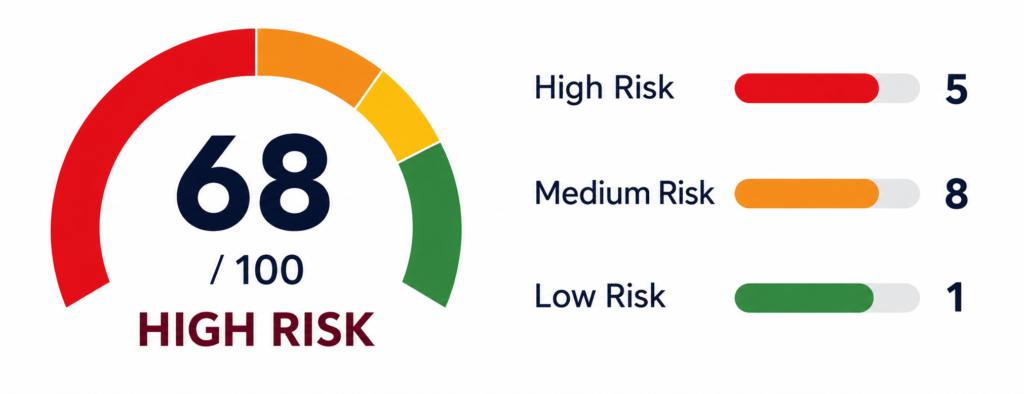
5 high-risk areas require immediate attention.
2. Overall Risk Overview
Visual summary of risk distribution across assessment areas.
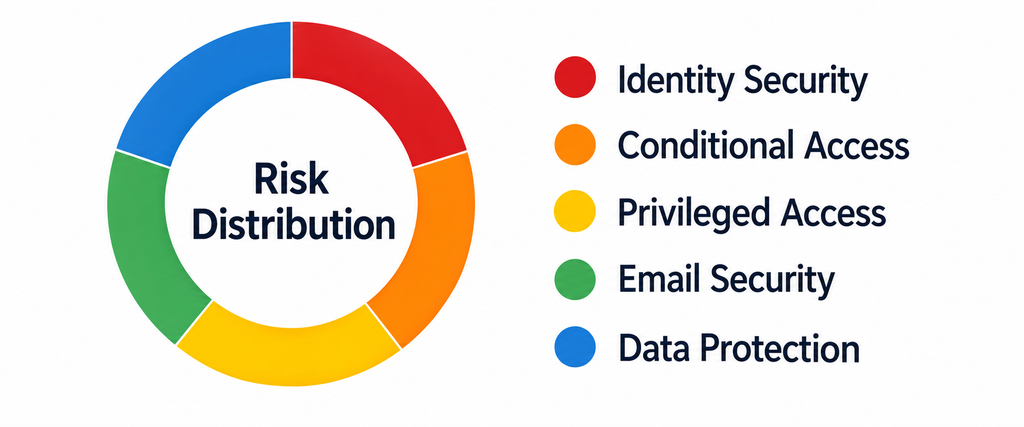
Risk distributed across identity, access, data, and governance.
3. Priority Action Plan (Next 30 Days)
Immediate actions to reduce exposure and strengthen your security foundation.
Focused, high-impact actions to address the most critical tasks identified in your environment.
These prioritized steps are designed to quickly reduce exposure, close security gaps, and strengthen your Microsoft 365 foundation.
Targeted actions that deliver the greatest risk reduction.
4. Key Findings
Examples of critical issues identified during the assessment.
High-risk identity and access gaps were detected that increase exposure to account compromise.
Legacy authentication and insecure settings create unnecessary risk.
Email security and domain authentication controls need attention.
Findings are validated and prioritized by risk and impact.
5. Risk & Governance Dashboard
Snapshot of risk posture and maturity across core domains.
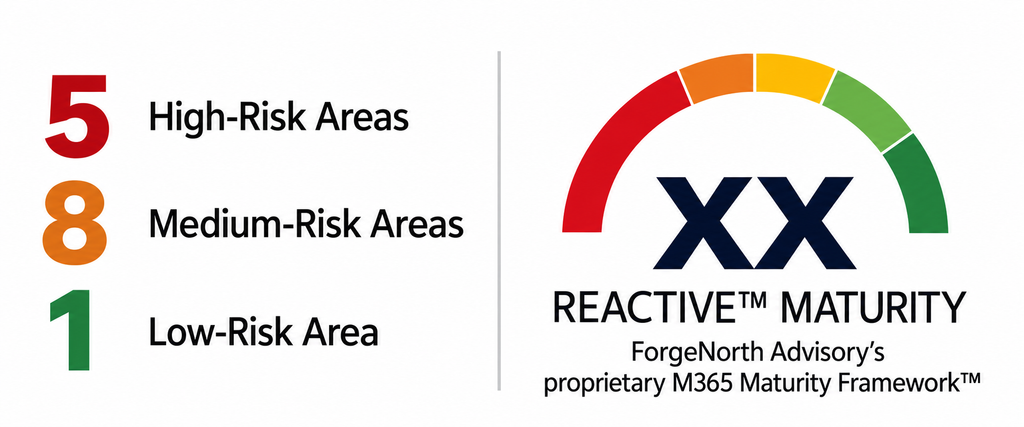
Understand your maturity and where to focus next.
6. Recommended Remediation Roadmap
Prioritized roadmap on risk, impact, and effort.
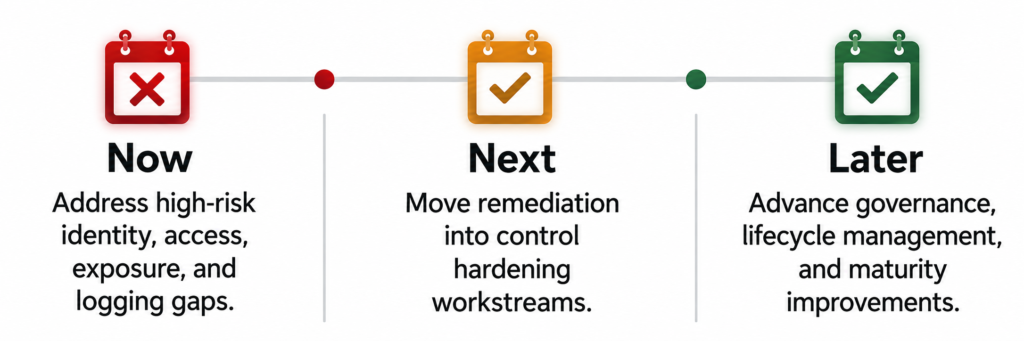
A phased plan aligned to quick wins and long-term improvement.
Not Sure Which Service Fits?